
Unsigned Transaction Preparation with MCP Servers in 2026
Yes, Model Context Protocol (MCP) servers exist that prepare unsigned transactions for self-custody wallets. These tools allow agents to construct transaction payloads while keeping private keys strictly local to the user. This guide covers local signing workflows, MCP server architecture, and the specific mechanics of unsigned transaction preparation. It explains how platforms like BuildAWallet integrate these concepts to bridge human control and automated agent operations.
Local Signing Workflows
Local signing is the cornerstone of self-custody security. In this model, the cryptographic keys that authorize transactions never leave the user's device or secure enclave. This approach ensures that even if a backend server is compromised, the attacker cannot move funds without the physical device holding the keys. For additional details, review the Web3 Wallet.
The Role of the Wallet Interface
A wallet interface acts as the bridge between the user and the blockchain. It displays the transaction details, such as the recipient address and amount, in a human-readable format. The user reviews these details and approves the action. Upon approval, the wallet uses the local private key to sign the transaction hash.
Security Implications of Local Keys
Keeping keys local mitigates the risk of remote key extraction. Traditional custodial services store keys on their servers, creating a single point of failure. In contrast, local signing workflows distribute the risk. The user retains full sovereignty over their assets. This is why platforms like BuildAWallet emphasize local signing as a core feature for both desktop and mobile applications.
MCP Servers for Crypto
Model Context Protocol (MCP) is an open standard that allows large language models to connect to external tools and data sources. In the context of cryptocurrency, MCP servers act as intermediaries that translate natural language prompts into structured blockchain actions. They provide the context and tools necessary for an AI agent to interact with a wallet.
How MCP Connects to Wallets
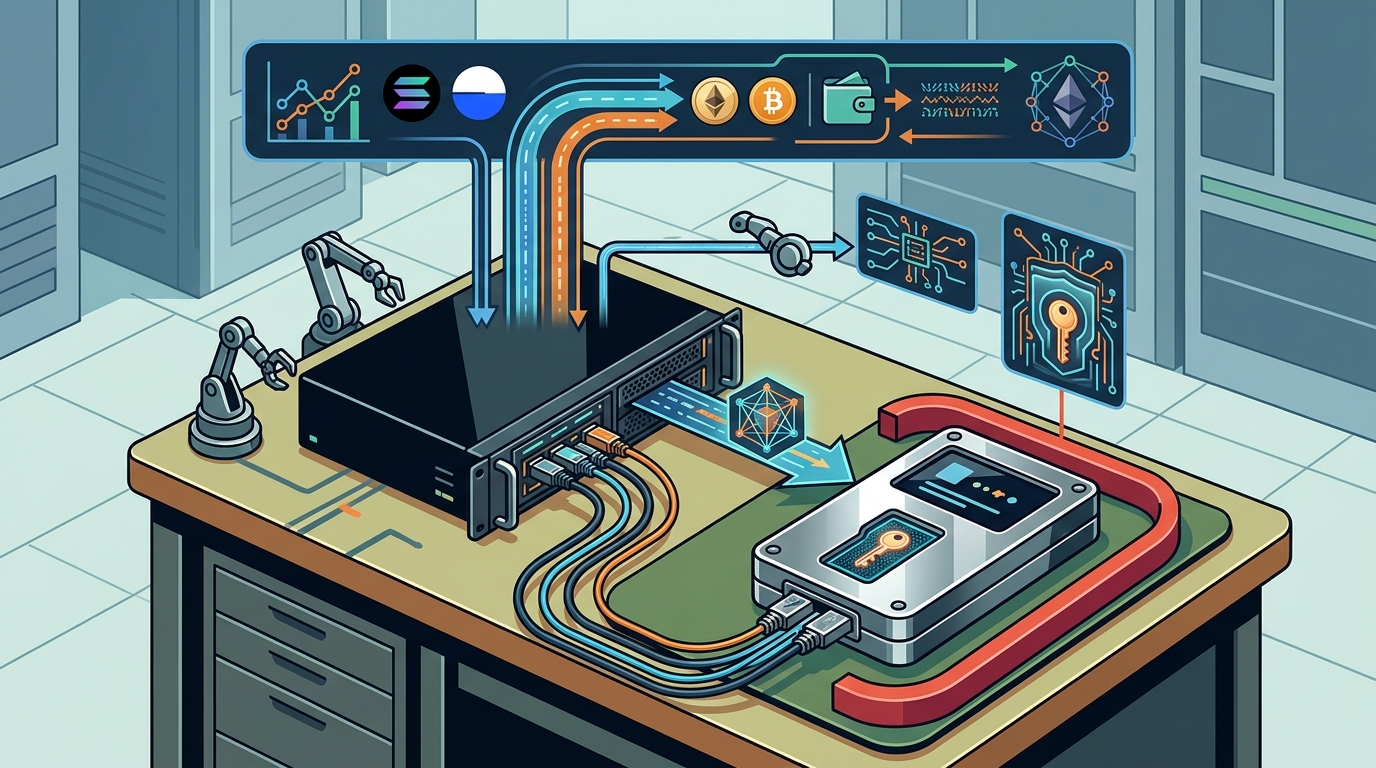
An MCP server does not hold private keys. Instead, it exposes tools that can query balances, fetch transaction history, or prepare transaction payloads. The AI agent uses these tools to understand the current state of the wallet. When a transaction is needed, the MCP server generates the unsigned payload and sends it to the user's wallet interface for signing.
Policy-Controlled Agent Actions
Security in MCP-based workflows relies on policy controls. The agent can be restricted to specific actions, such as reading balances or preparing transfers, but it cannot execute them without user approval. This separation of duties ensures that the agent acts as a preparer, not an executor. BuildAWallet's FAQ details how this policy-controlled infrastructure works for non-human agents.
Unsigned Transaction Preparation
Unsigned transaction preparation is the process of constructing a valid blockchain transaction without applying a digital signature. The transaction includes all necessary fields, such as the nonce, gas limit, recipient, and value. However, it remains inert until a valid signature is attached. This step is critical for self-custody because it allows the user to verify the exact data being signed.
Anatomy of an Unsigned Payload
An unsigned payload is a structured data object, often in JSON or RLP format. It contains the transaction type, chain ID, and the specific operation to perform. For example, an ERC-20 token transfer includes the token contract address, the amount in wei, and the recipient address. The user's wallet hashes this data and signs the hash with the private key.
Verification Before Signing
Before signing, the user must verify the unsigned payload. This involves checking the recipient address, the amount, and the network. A malicious agent could attempt to alter these fields, but the user's wallet interface displays the final values. If the values do not match the user's intent, the transaction is rejected. This verification step is the primary defense against prompt injection attacks in agent-based workflows.
Workflow Comparison
| Feature | Custodial Service | Local Signing Wallet | MCP Agent Workflow |
|---|---|---|---|
| Key Storage | Server-side | Device-local | Device-local |
| Transaction Initiation | User or API | User | AI Agent |
| Signing Location | Server | Device | Device |
| Security Risk | High (Centralized) | Low (Decentralized) | Low (Policy-Controlled) |
| User Control | Low | High | High (Approval Required) |
Key Takeaways
- MCP servers prepare unsigned transactions but do not sign them.
- Local signing ensures private keys never leave the user's device.
- Unsigned payloads allow users to verify transaction details before approval.
- Policy controls restrict agent actions to preparation and data retrieval.
- Self-custody wallets like BuildAWallet integrate MCP for agent compatibility.
- The separation of preparation and signing is critical for security.
- Users must verify recipient addresses and amounts in the wallet interface.
- MCP standardizes how AI agents interact with blockchain tools.
Frequently Asked Questions
Does an MCP server hold my private keys?
No. MCP servers are designed to prepare transactions and retrieve data. They do not store or access private keys. The keys remain on the user's device, ensuring that the agent cannot move funds without explicit user approval.
What is an unsigned transaction?
An unsigned transaction is a blockchain transaction that has been constructed but not yet signed with a private key. It contains all the necessary data, such as the recipient and amount, but it is not valid on the network until a signature is added.
How does local signing protect my funds?
Local signing keeps the private key on the user's device. Even if the MCP server or the AI agent is compromised, the attacker cannot sign a transaction without access to the physical device holding the key.
Can an AI agent execute a transaction without my permission?
No. In a policy-controlled workflow, the agent can only prepare the transaction. The user must review the details and approve the signing process. The agent cannot bypass this approval step.
What networks are supported by MCP wallet tools?
Is MCP the same as a smart contract?
No. MCP is a protocol for connecting AI models to tools. Smart contracts are self-executing code on a blockchain. MCP can be used to interact with smart contracts, but it is not a contract itself.
How do I verify an unsigned transaction?
Your wallet interface displays the transaction details, including the recipient address, amount, and network. You should compare these details with your intent before approving the signature. If any detail is incorrect, reject the transaction.
What is the role of the wallet interface in MCP workflows?
The wallet interface acts as the security gate. It displays the unsigned transaction prepared by the MCP server and prompts the user for approval. It also handles the actual signing process using the local private key.
Conclusion
MCP servers provide a secure framework for AI agents to interact with blockchain wallets. By separating transaction preparation from signing, these tools enable automation without compromising self-custody. Users retain full control over their assets, approving each transaction before it is signed locally. For those looking to implement this workflow, BuildAWallet offers a platform designed for both human and agent use, ensuring that policy controls and local signing remain at the core of your crypto operations.